365PK Game
1.1.74 / version code 12
6.74 MB
1.1.74
Android 6.0 / API 23 or newer
Description
Account Security & Permission Audit
Table of Contents
365PK Game is an Android APK that can be examined at the package and permission level. This 365PK Game review focuses on the supplied APK rather than copying technical specifications from third-party download pages.
| Detail | Verified Information |
|---|---|
| App | 365PK Game |
| Version | 1.1.74 |
| Version Code | 12 |
| Package Name | com.jkcg.fswrh3929.jtoby |
| APK Size | 7,068,880 bytes (~6.74 MiB) |
| Minimum Android | Android 6.0 / API 23 |
| Target SDK | API 34 / Android 14 |
| Compile SDK | API 34 |
| Architectures | armeabi-v7a + arm64-v8a |
| Main Activity | com.speed.client.CCMainActivity |
| Web Activity | com.speed.client.CCWebActivity |
| Application Class | com.speed.client.CCAppClient |
| Site Code | s3929 |
| SHA-256 | ef35f09416879a7f39b54660c02e1a4373bd0c35d0aabc6c61eb634d795e3fe5 |
These values identify the particular APK analyzed for this article. They should not automatically be applied to every file available online under the 365PK Game name.
What This 365PK Game Security Audit Checks
A normal APK article often lists features and a download button without examining what the Android package actually requests.
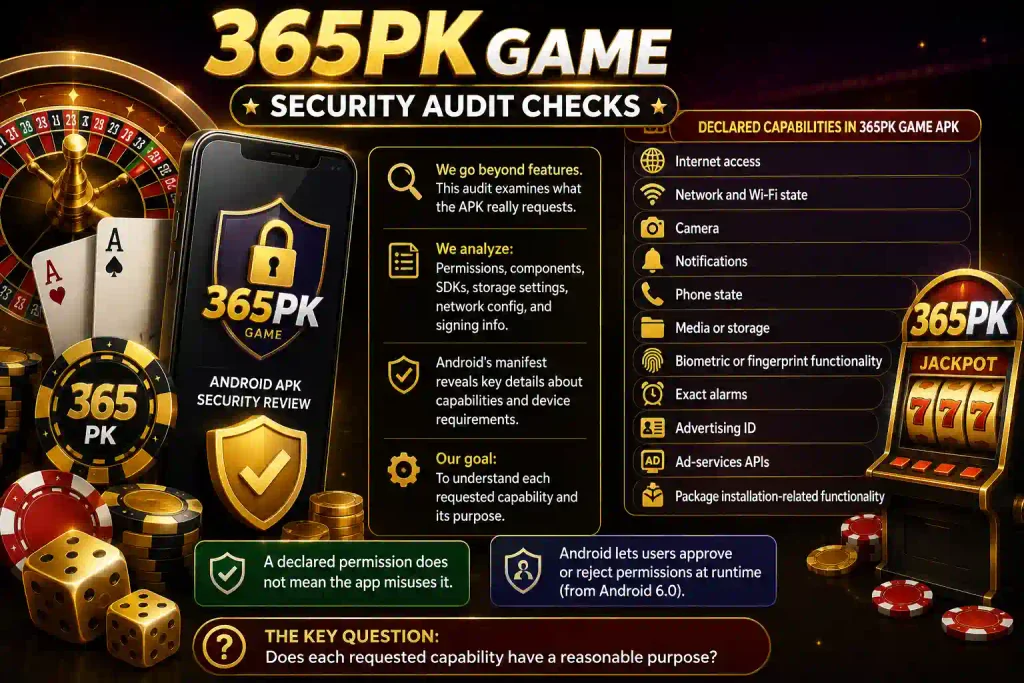
This 365PK Game audit takes a different approach. It looks at the APK’s declared permissions, application components, SDK integrations, storage settings, network configuration, and signing information.
Android’s manifest contains important information about an application’s components, permissions, and required device capabilities.
The supplied APK declares capabilities involving:
- Internet access
- Network and Wi-Fi state
- Camera
- Notifications
- Phone state
- Media or storage
- Biometric or fingerprint functionality
- Exact alarms
- Advertising ID
- Ad-services APIs
- Package installation-related functionality
A declared permission does not automatically mean that an app is abusing that capability.
Android allows users to approve or reject applicable permissions at runtime, starting with Android 6.0 for the relevant permission model.
The important question is therefore whether each requested capability has a reasonable purpose.
365PK Game Internet Permission
Internet access is an expected requirement for an online application.
The supplied 365PK Game APK contains network-related permissions and components. These can allow the application to communicate with remote servers and check network availability.
For an online game, this may be required for account communication, game data, configuration, messaging, analytics, or other server-based functions.
However, the manifest does not tell us everything about the application’s network behavior.
Static APK analysis cannot by itself establish exactly which personal information is transmitted, which servers receive it, or whether every connection uses encryption.
Therefore, internet access should be treated as a verified technical capability, not evidence of malicious activity.
365PK Game Camera Access
Camera capability is another declared feature in the APK.
The supplied analysis also identifies an optional camera hardware declaration.
Camera access can have legitimate uses in an Android application. Depending on the application’s design, it could support functions such as scanning, profile features, verification, or other camera-based functions.
The presence of the permission does not prove that 365PK Game continuously records through the camera.
Android’s permission system is designed to give users control over applicable sensitive access.
If 365PK Game asks for camera access, users should consider whether the feature they are using actually requires it.
Phone State Permission
The APK also declares phone-state-related capability.
This category can cover different device or telephony information depending on the exact Android API being used.
Such access deserves attention because information about a device or its telephony environment can be sensitive.
However, the APK declaration alone does not prove exactly what phone information is collected or stored.
For users, the practical step is to review the permission request shown by Android and avoid granting unnecessary access.
Media and Storage Access
The supplied APK contains media or storage-related capabilities.
Storage permissions can be useful for applications that need to read or write files, but broad access can also have privacy implications.
Google’s Android guidance treats access to user files and directories as sensitive and recommends that applications request only the storage access needed for their core functionality.
The 365PK Game APK also declares:
requestLegacyExternalStorage="true"
This is an important technical finding.
It is associated with compatibility for older external-storage behavior. Its presence should not be described as proof that the application is unsafe.
The exact effect can also depend on the Android version and the application’s implementation.
Biometric and Fingerprint Capability
Biometric-related components are present in the supplied APK.
Biometric functionality can be used for authentication or confirmation on supported Android devices.
This does not mean the APK has been shown to collect raw fingerprint information.
The presence of biometric APIs only tells us that the application includes components capable of interacting with Android’s biometric functionality.
For account security, users should still use their device’s normal biometric controls and avoid sharing passwords, PINs, or OTP codes with other people.
Notification Access
Notification-related capability is also declared.
Notifications can be used for account messages, game updates, reminders, promotional messages, or other alerts.
This is not normally considered equivalent to access to highly sensitive device resources such as camera or storage.
Users can control notification behavior through Android’s application settings if they do not want frequent alerts.
Advertising ID and Ad-Services Components
The supplied APK contains advertising-related components, including advertising ID and ad-services functionality.
These technologies can be used for advertising, attribution, measurement, or related purposes.
The presence of these components does not establish that 365PK Game is collecting a particular type of personal information.
It also does not prove that every included SDK function is active.
The technically accurate conclusion is simply that advertising-related functionality is present in the analyzed package.
Users who are concerned about privacy should review the application’s privacy information and the privacy controls available on their Android device.
Third-Party SDKs Inside 365PK Game
The APK contains components associated with several third-party services and SDKs.
The supplied analysis identifies:
- Firebase
- Facebook SDK
- Adjust
- AppsFlyer
- Bugsnag
- Sensors Analytics
- Zalo
- EngageLab
These SDKs can serve different purposes.
Analytics services may provide usage measurement. Attribution platforms can help developers understand advertising campaigns. Error-reporting tools can help identify crashes. Messaging components can support notifications or communication.
Their presence alone does not prove exactly how each service is being used.
For this reason, the 365PK Game audit records these components as observed APK integrations, rather than claiming that the application definitely sends a specific type of user data to every listed service.
365PK Game and Cleartext Traffic
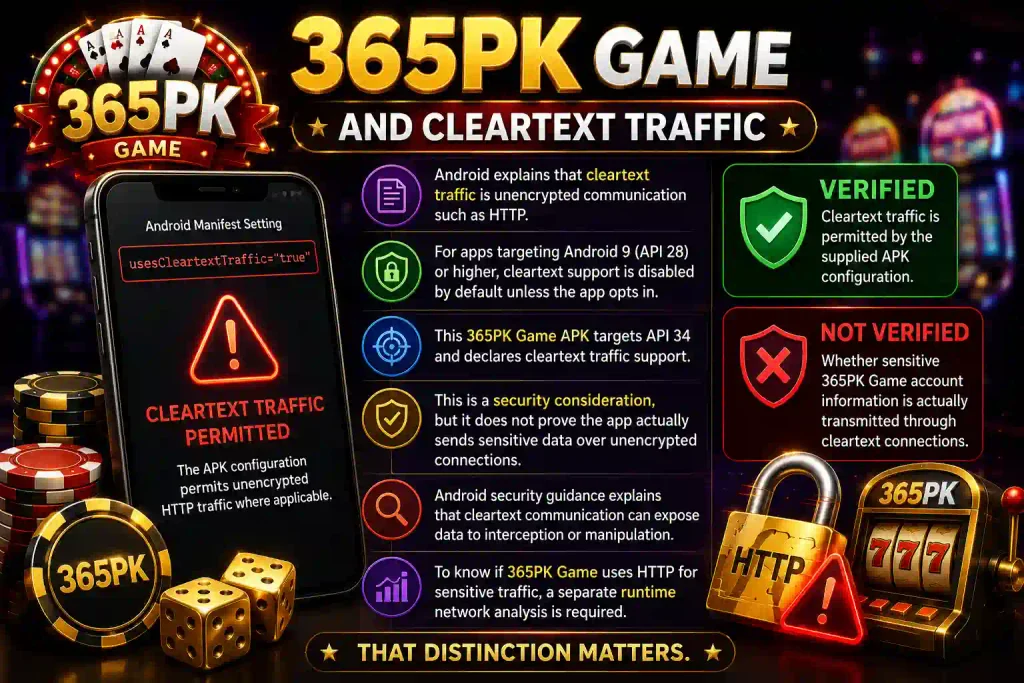
One of the most important findings in the supplied APK is:
usesCleartextTraffic="true"
This setting deserves closer attention.
Android documentation explains that cleartext traffic refers to communication such as unencrypted HTTP. For applications targeting Android 9/API 28 or higher, cleartext support is disabled by default unless the application opts in.
The analyzed 365PK Game APK targets API 34 and declares cleartext traffic support.
That means the APK configuration permits cleartext traffic where applicable.
This is a security consideration, but it does not prove that the application actually sends passwords, account details, payment information, or other sensitive data through unencrypted connections.
Android’s security guidance explains that cleartext communication can expose transmitted information to interception or manipulation.
To determine whether 365PK Game actually uses HTTP for sensitive traffic, a separate runtime network analysis would be required.
Therefore:
Verified: Cleartext traffic is permitted by the supplied APK configuration.
Not verified: Whether sensitive 365PK Game account information is actually transmitted through cleartext connections.
That distinction matters.
365PK Game and allowBackup
The supplied APK also declares:
allowBackup="true"
Android describes this setting as controlling whether an application can participate in backup and restore infrastructure.
Backup can be useful when users move between devices or restore application information.
However, this setting alone does not tell us which specific 365PK Game data is included in a backup.
It therefore would be inaccurate to claim that passwords, payment details, or account information are automatically exposed because allowBackup is enabled.
The correct finding is that backup participation is enabled in the analyzed application configuration.
Package Installation-Related Capability
The APK also contains package installation-related permissions or components.
This is worth documenting because package installation capabilities can have security implications.
However, the presence of such a declaration does not prove that 365PK Game installs other applications.
A deeper investigation would need to examine the relevant code paths, intents, components, and actual runtime behavior.
Users should generally be cautious when an unfamiliar application asks for permission to install additional packages.
Remote Configuration in 365PK Game
The supplied APK contains references to a remote configuration mechanism involving two config_data.json locations.
This is significant because it indicates that some application or game configuration may be retrieved remotely instead of being permanently stored inside the APK.
Remote configuration is not unusual.
Developers can use it to change application settings or content without rebuilding and distributing the entire application.
For 365PK Game, this means the APK should be viewed as a snapshot of the application package rather than a complete description of every possible runtime configuration.
It also means that static analysis cannot answer every question about the application’s behavior.
Cocos2d-x and Native Libraries
The APK includes native libraries for:
armeabi-v7aarm64-v8a
The supplied analysis also identifies strings and components associated with Cocos2d-x-related game infrastructure.
This suggests that native game technology is part of the application’s technical structure.
Supporting both ARM variants can improve compatibility across different Android hardware.
Native libraries are common in games and do not, by themselves, indicate malware or another security problem.
365PK Game Signing Certificate
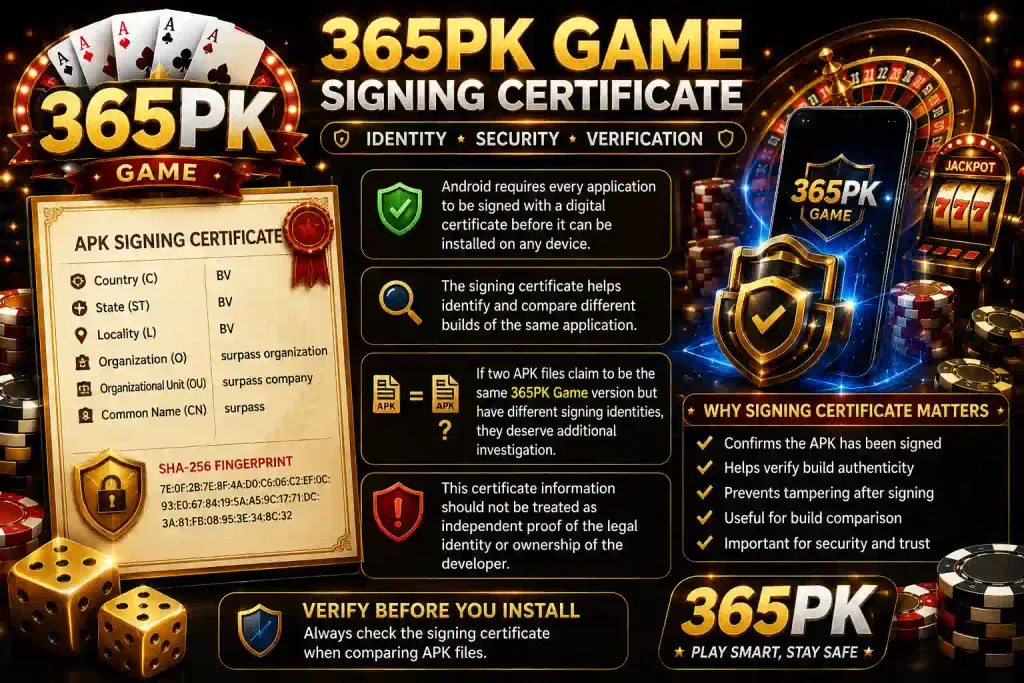
The analyzed APK is signed with a certificate containing the following identity information:
Country: BV
State: BV
Locality: BV
Organization: surpass organization
Organizational Unit: surpass company
Common Name: surpass
The supplied certificate SHA-256 fingerprint is:
7E:0F:2B:7E:8F:4A:D0:C6:06:C2:EF:0C:93:E0:67:84:19:5A:A5:9C:17:71:DC:3A:81:FB:08:95:3E:34:8C:32
Android requires applications to be signed, and the signing certificate can help identify and compare application builds.
This information is useful when comparing multiple APK files.
For example, if two files claim to be the same 365PK Game version but have different signing identities, they deserve additional investigation.
The certificate information should not, however, be treated as independent proof of the legal identity or ownership of the developer.
365PK Game APK SHA-256
The supplied APK has this SHA-256 hash:
ef35f09416879a7f39b54660c02e1a4373bd0c35d0aabc6c61eb634d795e3fe5
A SHA-256 hash can be used as a file fingerprint.
If another 365PK Game APK produces the same SHA-256 value, the files are identical at the byte level.
If the hashes differ, the files are different.
A different hash alone does not prove that another file is malicious. It simply indicates that the APK contents are not identical.
For users comparing APK sources, the combination of version, package name, file size, signing certificate, and SHA-256 provides a much stronger basis for identifying a particular build.
Does This Audit Prove 365PK Game Is Safe?
No.
It would be inaccurate to call 365PK Game completely safe based only on static APK analysis.
It would also be inaccurate to call it malware simply because the application requests several permissions.
The supplied APK provides strong technical evidence about its package identity and configuration. It does not independently verify every server connection, every SDK operation, or the application’s complete runtime behavior.
The most notable security consideration is the declared cleartext-traffic setting.
The APK also contains several sensitive capabilities and third-party components that users should understand before installation.
The appropriate conclusion is therefore:
The supplied 365PK Game APK has identifiable technical characteristics and several permissions worth reviewing. The static evidence available for this audit is not sufficient to establish either complete safety or malicious behavior.
365PK Game Account Security Checklist
Before creating or using an account, users should take a few basic precautions.
1. Verify the APK File
Check the source of the APK before installing it.
Avoid assuming that every file carrying the 365PK Game name is the same application.
2. Check the Package Name
The analyzed package name is:
com.jkcg.fswrh3929.jtoby
This can help distinguish the analyzed build from similarly named applications.
3. Compare the Version
The analyzed version is 1.1.74, with version code 12.
If another source lists a different version, do not assume that both files are identical.
4. Review Android Permissions
Pay attention when 365PK Game requests access to the camera, storage or media, phone-related information, or other protected features.
Grant access only when the requested feature requires it.
5. Protect Your Login Details
Never share your password, OTP, PIN, or other account credentials with another person.
A legitimate application should not require you to disclose an OTP to an unrelated person.
6. Be Careful With Payment Information
The APK analysis does not independently verify Easypaisa, JazzCash, bank-transfer support, withdrawal limits, or earning amounts.
Technical APK information should not be treated as proof of payment reliability.
7. Keep Android Updated
Using an updated Android version can provide newer security protections and permission controls.
What Is Verified and What Is Not?
Verified From the Supplied APK
- Version 1.1.74
- Version code 12
- Package name
- APK size
- Minimum Android version
- Target SDK
- Compile SDK
- ARM architectures
- Main activity
- Web activity
- Application class
- Site code
- SHA-256
- Declared permission/capability categories
- Third-party SDK/component presence
- Cocos2d-x-related components
- Remote configuration references
usesCleartextTraffic="true"allowBackup="true"requestLegacyExternalStorage="true"- Signing certificate information
Not Independently Verified
- Guaranteed earnings
- Guaranteed winnings
- Guaranteed withdrawals
- Specific bonus amounts
- Easypaisa support
- JazzCash support
- Bank-transfer support
- Exact runtime network traffic
- Exact data collected by each third-party SDK
- Actual use of cleartext HTTP for sensitive information
- Developer’s legal ownership based solely on the signing certificate
- Whether every APK found online under the 365PK Game name is the same build
Keeping these two groups separate is important for an accurate 365PK Game security assessment.
365PK Game Final Security Assessment
The supplied 365PK Game APK provides considerably more information than a basic download-page specification.
The analyzed build is version 1.1.74, version code 12, with package name com.jkcg.fswrh3929.jtoby and an APK size of approximately 6.74 MiB. It supports ARMv7 and ARM64 devices, requires Android 6.0/API 23 or newer, and targets API 34.
From an account-security perspective, the main areas that deserve attention are its camera, phone-state, storage or media, biometric, notification, advertising, and package installation-related capabilities.
The APK also contains several third-party SDKs and services, native game libraries, remote configuration references, and a recognizable signing certificate.
The usesCleartextTraffic="true" configuration is particularly worth noting because cleartext communication can expose data to interception when it is actually used. Android recommends secure network communication, but the manifest setting alone does not prove that 365PK Game sends sensitive information through unencrypted connections.
Likewise, allowBackup="true" is a configuration setting and does not prove that sensitive account information is exposed through backups.
Overall, the supplied evidence supports a cautious technical assessment rather than a simple safe-or-dangerous label. Users should verify the APK source, compare package and hash information, review permissions, protect their account credentials, and avoid treating unverified earning or payment claims as established facts.
For additional APK and safety-related reading, APKSpin’s existing 3R3R Game APK and CT777 Game articles provide related examples of APK-focused investigation.
For Android’s official technical guidance, readers can also consult Android’s permission documentation, Network Security Configuration, and the Android application manifest reference. These sources provide the technical background for understanding the permission, backup, and network-security findings discussed above.